Company overview · Stealth Castle (SMTD)

Defending against AI‑automated hacking …
active defense is the answer

"The proven secret weapon" Stealth Castle (SMTD)

Videos Contact us
≤1sAddress mutation interval
0Successful attacks · bank red team AI test

1 · The attacks have begun

AI-automated hacking: the attacks have already begun

In September–October 2026, attacks using an AI penetration agent breached seven Korean financial companies

Financial companies breached

7

Banks, savings banks, capital firms

Customers affected

68K

About 66,000–70,000 depending on the count date

Core banking systems were untouched — the breaches came through externally visible touchpoints alone

Sources Financial News 2026-10-04·10-07; Herald Economy 2026-10-03

1.2 · ARTEX

What ARTEX did — from automated reconnaissance to mass queries

  1. Auto reconScan exposed addresses and services
  2. BypassPick the weakest touchpoint
  3. Credential stuffingReplay leaked accounts
  4. EvasionRotate IPs, try in small volumes
  5. Mass queriesExfiltrate by querying, no takeover

If the first step cannot find a target, the later steps never start

Note ARTEX: an open-source penetration agent chaining external LLMs such as DeepSeek (confirmed by the Financial Security Institute). Credential stuffing is presumed

Sources FP Table 3; Herald Economy 2026-10-03; Money Today 2026-10-02

2 · Why it is dangerous

Why is AI-automated hacking dangerous?

AI did not change the techniques — it made them cheaper, faster and more numerous

Tactical work done by AI

80–90%

Humans only at 4–6 decision points

Reproduced by a non-expert

6min

Public model, one GPU

Fastest lateral spread

27s

Faster than human monitoring

Sources Anthropic threat report 2025-11-13; ZDNet Korea 2026-10-06 (Soongsil Univ. simulation); CrowdStrike 2026 Global Threat Report

2.2 · LIMITS

Building higher walls cannot stop it

Firewall · IDS · detectionDetect, then block — after the fact
  • Blocks only after seeing the intrusion
  • Low-volume attempts below the rules pass through
Static IPs and portsThe map is public
  • Addresses never change, so reconnaissance stays valid
  • Some firms only noticed after attack IPs were shared with them

Even globally, technology that erases reconnaissance itself is still an empty space

Note Globally, widely deployed ZTNA, endpoint MTD and AI detection protect only private apps, memory, or the post-detection phase respectively (within public sources)

Sources FP Table 4; New Daily 2026-10-08; Zscaler 10-K FY2026; morphisec.com; NIST SP 800-160 Vol.2 Rev.1

3 · The secret weapon

Defending against AI-automated hacking:
why is Stealth Castle (SMTD) the "secret weapon"?

Attackers cannot attack what they cannot find.
We hide, we trust no one, and we build bulkheads.

Sources FP Table 1; KR s13

3.1 · MOVING TARGET

Stealth Castle makes the castle invisible —
its address changes every second

Conventional — static targetThe address stays the same
  • An IP/port found once stays valid
  • Answers anyone's scan
Stealth Castle — moving targetThe address keeps changing
  • IPs and ports mutate as often as every second
  • No response to requests without a Knock

Note Mutation terminates at the gateway's external interface — back-end systems keep their static addresses and firewall policies stay unchanged · Sources KR s13·s14·s18; AR v3.0 p4·p6

3.2 · ZERO TRUST

Stealth Castle
trusts no one

Zero Trust through 5-vector authentication

Five vectors verified together in the OS kernel

PIDRunning process
SessionConnection session
App metaApp integrity
UserUser authentication
DeviceDevice authentication

The five vectors form an "application identity", and unauthorized processes on infected devices are isolated

Sources KR s15; L05 p12

3.3 · MICRO SEGMENTATION

Stealth Castle builds
bulkheads inside the castle

Micro segmentation, App to App

Network-segment basedInside a segment, everything is open
  • Hosts in the same segment talk freely
  • One breached host spreads laterally
App to AppOnly approved apps are connected
  • Variable multi-tunnels only between app pairs
  • Blocks lateral movement · non-disruptive OT overlay

Abnormal access is lured into a decoy to collect attack behavior

Sources KR s12·s17; Seoul Metropolitan Government active-security proposal §3.2 (2026-09-11)

3.4 · RED TEAM PROOF

Stealth Castle vs. AI hacking
— "proven by a bank"

AI white-hat hacking (ARTEX) by a Korean bank's red team, October 2026

0

Successful attacksNo successful connection in the logs
3 rounds · external network · firewall opened · fixed IP

RoundConditionResult
1Existing security systems + Stealth CastleRecon failed · 0 successful attacks
2Existing security disabled, Stealth Castle onlyRecon failed · 0 successful attacks
3Fixed IP, only ports mutatedRecon failed · 0 successful attacks

3.5 · TRACK RECORD

Stealth Castle, a "security masterpiece"

Supplied to the military and public sector; this year we are pursuing contracts with financial companies

  1. 2021–22

    ROKAF 20th Fighter WingActive defense for video surveillance
  2. 2021–25

    ROK Army tactical networkActive defense for authentication servers
  3. 2023–24

    Seoul pilot0 exposed IPs/ports
  4. 2026

    Financial companies (OO Bank, △△ Card, etc.)Contracts in progress after pilots
  5. 2026

    Group AZero Trust project in progress
3 certifications · NET·NEP·GS Grade 1U.S. patent granted (2026-09-09)Multiple SCI-level papers submitted

Note Names of financial customers and Group A are withheld · Sources KR s27; Seoul proposal §4.2; IR08 s10; USPTO 2026-09-22 (company-provided)

3.6 · GLOBAL CONTEXT

In the U.S., active defense has long been a priority

  1. 2011

    White House NSTCCore R&D theme
  2. 2020

    NIST 800-53Security control SC-30(3)
  3. 2026

    NIST 800-172r3MTD requirement retained

Commercial vendors exist for memory mutation (Morphisec and others), but Stealth Castle is the one that has commercialized network mutation and deployed it in the field.Based on public sources — no network-MTD vendor has published customers or performance figures (2026-10-08). NIST includes MTD as an optional control

Sources NSTC 2011; NIST SP 800-53r5·800-172r3; morphisec.com; BusinessWire (Dispersive) 2026-03-09

4 · AEGIS

Stealth's other secret weapon:
AEGIS homomorphic encryption (AEGIS FHE)

Quantum-resistant encryption — compute, analyze and search while data stays encrypted

  1. PlaintextOriginal data
  2. EncryptAGCD-based, quantum-resistant
  3. Compute on ciphertextCompute · statistics · search
  4. Decrypt results onlyOriginal never exposed

Near real-time processing · healthcare, finance (credit scoring), public sector — first practical noiseless implementation in Korea

4.2 · BENCHMARK

Speed and error — past the wall of homomorphic encryption

In-house measurement on a degree-10 polynomial — before third-party verification

ConventionalSlow, and errors accumulate
  • Degree-10 operation 0.7997 s
  • Degree-10 error 0.0000052
AEGISFast, with zero error
  • Degree-10 operation 0.0075 s — 107× faster
  • Zero error · sum of 10,000 records matches to 25 decimal places

5 · The best combination

The best combination against AI hacking

"Wrap with AEGIS, shield with Stealth Castle"

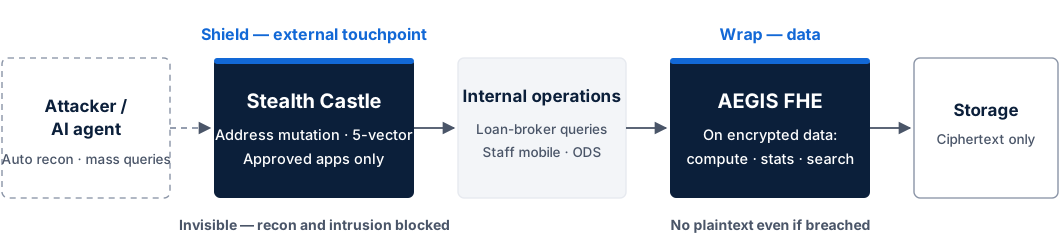
Attacker / AI agent → Stealth Castle at the external touchpoint (address mutation, 5-vector authentication, approved apps only) → internal operations and queries → AEGIS homomorphic encryption (compute, statistics and search on encrypted data) → storage and response (ciphertext only)
Conceptual architecture — the scope of application is determined during the pilot

Stealth Castle hides the external touchpoints, and AEGIS protects any data that leaves — without plaintext

Sources KR s9·s14·s20; AR v3.0 p4

Solution

Security solutions we also supply

Dark web intelligence · security automation · privacy security

Searchlight Cyber

CERBERUSDark web intelligence

Collect stronger evidence and strengthen security with dark web intelligence from the CERBERUS platform. Its automated analysis of underground resources improves an organization's response to cybercrime.

  • Dark web search — explore dark web data safely and prepare for threats
  • Evidence — collect evidence on ransomware, criminal and threat groups
  • Monitoring — watch active ransomware groups and suspicious actors
D3 Security

D3 SOARSecurity orchestration and automation

D3 SOAR, built on MITRE ATT&CK, is a SOAR (Security Orchestration, Automation and Response) platform that connects with many security vendors, giving SOC and response teams incident response, automation and threat intelligence in one place.

  • Codeless playbooks — configure and integrate by drag and drop
  • Integrates with a wide range of security systems
  • Automated correlation of attack techniques
FRENTREE

PICPersonal data discovery and security

PIC finds personal information on Windows, macOS and Linux servers and inside DBMS servers such as Oracle and Tibero, with a Korean-market web UI and a separate system for managing search results, built on experience scanning entire server fleets in the financial sector.

  • Minimal server impact — designed to use a single CPU core
  • Native format decoding — searches directly, without conversion or decompression
  • Result management — a separate management system

Source Previous company website, SOLUTION pages (archived 2026-10-11)

6 · Team

A proven technical and management team

A company built on defense and public-sector deployments since 2017

  1. 2017–18

    FoundedJoint research with ETRI
  2. 2019–20

    Pilots · PoCIncheon Airport, KT Cloud
  3. 2021–

    Defense supplyROKAF 20th FW · ROK Army network
  4. 2023–24

    Certification · publicNET·GS certified, Seoul pilot
  5. 2025–26

    NEP · U.S. patentNEP certified, U.S. patent granted

Stealth Solution Co., Ltd. · Co-CEOs Hyokeun Wang, Yuhan Park · Yeongdeungpo-gu, Seoul

Sources L05 p3; IR08 s10; KR s26·s27; Law Firm LIN press release 2026-07-08

6.2 · PEOPLE

A proven team — defense cyber operations, cryptographic mathematics,
information security academia and financial supervision

  • Yuhan Park, Co-CEO
    Co-CEOYuhan ParkCHA Biotech Group · former KBS Washington correspondent
  • Hee Han, CSO
    CSOHee HanPresident, Seoul Media Institute of Technology · former director, Korea Institute for Defense Analyses
  • Seok-Jin Kang, Head of R&D Center
    Head of R&D CenterSeok-Jin KangProfessor, Mathematical Sciences, Seoul National University · Korean Academy of Science and Technology
  • Byung-Do Lee, CTO
    CTOByung-Do LeeFormer center director, Cyber Operations Command · Professor, Cheongju University
  • Jun-Hwan Kim, Auditor
    AuditorJun-Hwan KimFormer Assistant Governor, Financial Supervisory Service
  • Attack verificationRed teamFormer center director and operations team lead, Cyber Operations Command

Note Titles as of IR08 s11 · Sources KR s26; IR08 s11; Law Firm LIN press release 2026-07-08 (red team); KC s11

Video

Videos

Click a thumbnail to open the YouTube (youtube-nocookie) player.

7 · Sources

Sources

Sources from each chapter, grouped by area

AreaMaterial
Incidents · threatsFinancial News 2026-10-04·10-07 · Herald Economy 10-03 · Money Today 10-02 · New Daily 10-08 · ZDNet Korea 10-06 · CrowdStrike 2026 GTR · Anthropic 2025-11-13
Global · U.S.Zscaler 10-K FY2026 · morphisec.com · BusinessWire (Dispersive) 2026-03-09 · NIST SP 800-53r5·800-160 Vol.2·800-172r3 · NSTC 2011
Company materialsKR company and technology overview (2026-10) · FP financial-sector proposal (2026-10) · AR security architecture v3.0 · IR08 · L05 · KC · Seoul proposal (2026-09-11) · Law Firm LIN press release (2026-07-08)
Tests · patents · otherRed team penetration test progress report (2026-10-08) · USPTO documents (2026-09-22) · AEGIS search evidence (confirmed by the CEO 2026-10-09) — company-provided

Contact

Contact

Co-CEOs
Hyokeun Wang, Yuhan Park
Address
1001, 10th floor, Cheonrok Building, 2, Yeouidaebang-ro 61-gil, Yeongdeungpo-gu, Seoul 07319, Korea
Subway
Daebang Station exit 7, 150 m to the left
Fax
+82-2-562-1228

Talk to us

For enquiries about SMTD (Stealth Castle), please e-mail us. A specialist will get back to you directly.

Please include your company, name, contact details and enquiry.

E-mail us